You can configure a local connection to suspend users' access automatically under specified rules. User accounts that match the conditions of a suspend rule no longer have access to resources and are shown in the account list as suspended.
Suspend rules are custom. You can base them on any attribute or combination of attributes passed by the local source. For example, if you manage users through SirsiDynix, you could base a rule on the SirsiDynix attribute patronStatusInfo.statusType. You do not need to map local attributes to OpenAthens attributes when using them in a suspend rule.
Suspend rules apply only to local user accounts.
Structure of a suspend rule
A suspend rule consists of one or more conditions. Each condition has three parts:
-
The local attribute on which the condition is based. For example, ‘role’ or ‘status’
-
The value against which to test the attribute. For example, ‘staff' or ‘inactive’
-
The test to perform. For example, ‘matches’, ‘contains' or ‘does not match’
If a rule has more than one condition, you can require any or all of the conditions to be true. If you specify any, users who meet at least one condition in the rule will be suspended. If you specify all, only users who meet all of the conditions will be suspended.
Example rules
Example 1
Suspend account when any of these conditions are met:
memberOf contains visitor
memberOf contains walk-in
Suspends user accounts whose memberOf attribute contains either of the values ‘visitor’ or ‘walk-in’.
Example 2
Suspend account when all of these conditions are met:
memberOf contains staff
memberOf contains temporary
Suspends user accounts whose memberOf attribute contains both of the values ‘staff’ and ‘temporary’.
Example 3
Suspend account when all of these conditions are met:
department does not match physics
department does not match chemistry
Suspends accounts for all users who belong to neither the physics nor chemistry departments.
Create a suspend rule
-
Log in to the Compass admin area (https://admin.openathens.net) as an administrator.
-
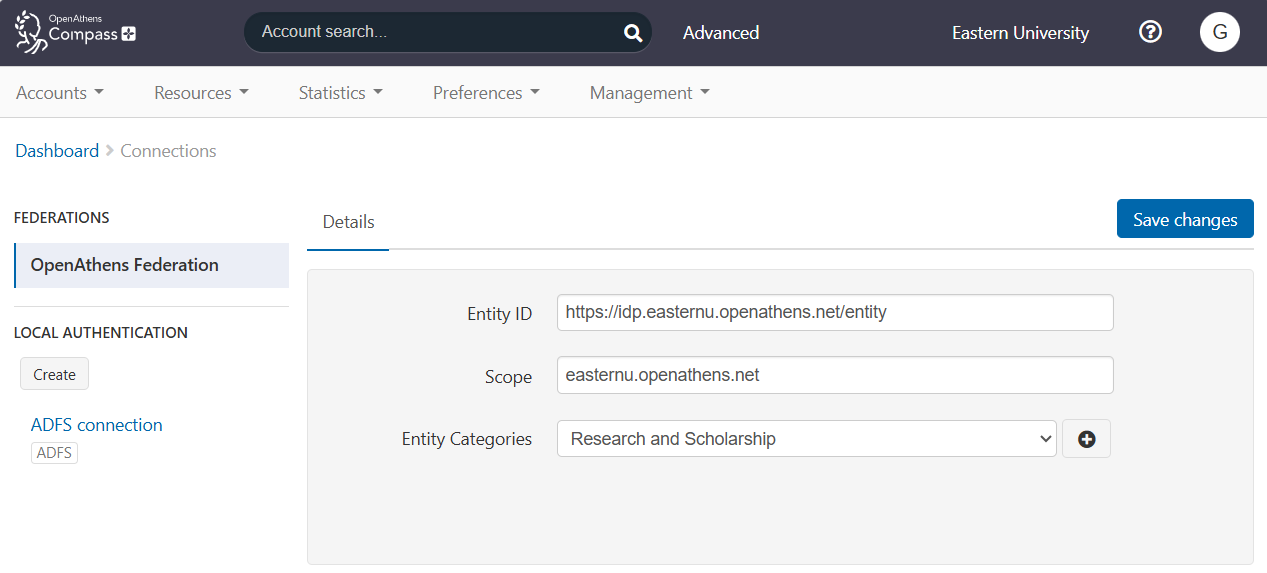
Go to Management > Connections.
-
Under Local authentication in the left sidebar, select your local connection to edit it.
-
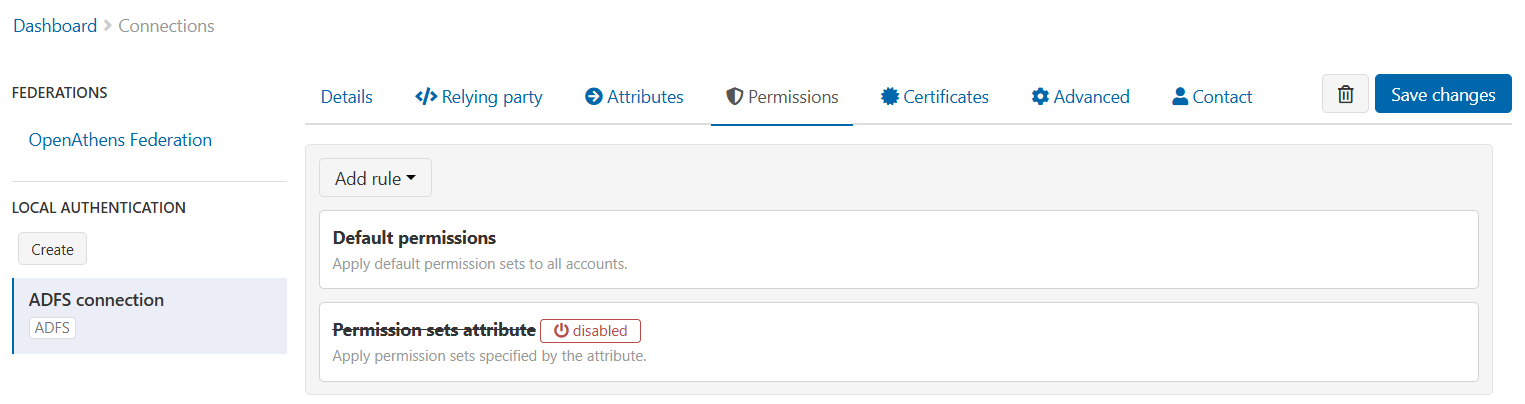
Go to the Permissions tab.
-
From the Add rule drop-down menu, select Suspend account.
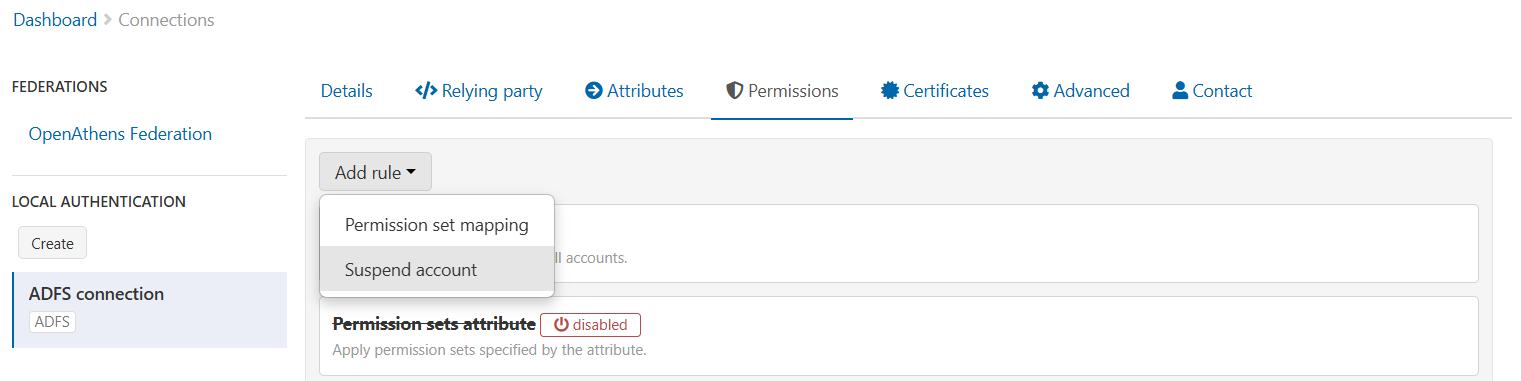
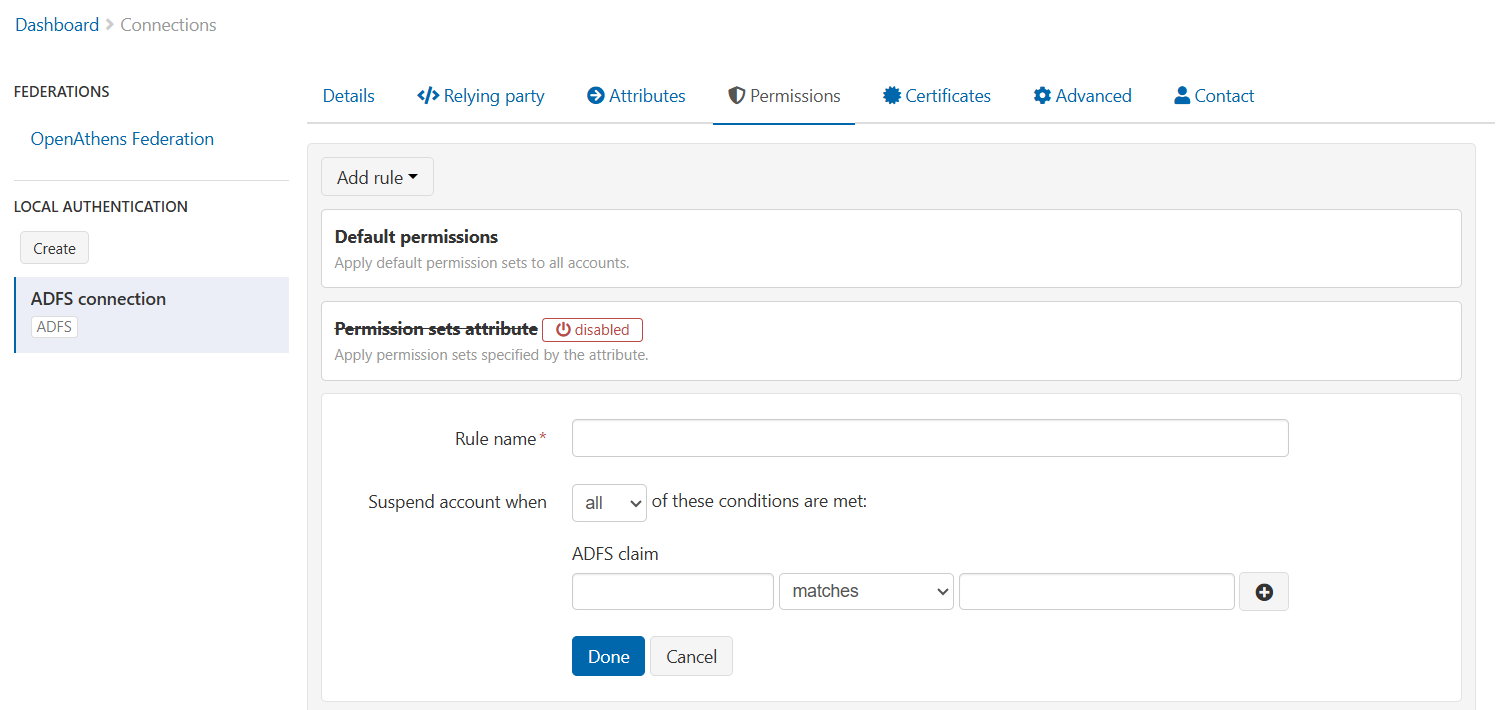
A template for creating a new suspend rule appears further down the page.
-
In the Rule name field, enter a descriptive name for this rule.

-
Under Suspend account when, define the conditions of the rule. For each condition, you need to choose a local attribute to evaluate, the test to perform on the attribute, and the value to compare it against.
First, from the drop-down menu, choose whether to match any or all of the specified conditions.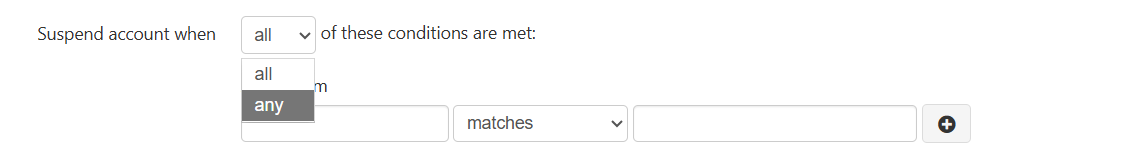
If you’re creating a simple rule with only one condition, you can choose either setting since they are effectively the same. If you’re creating a rule with more than one condition, select all to enforce the rule only if all of the specified conditions are met. Selecting any will enforce the rule if at least one of the conditions is met.
-
In the first input field, enter the name of the local attribute on which to base the rule. Use the name by which the attribute is called in the local source. Attribute names are case sensitive.
(In this example, the field is called ADFS claim. Its label will vary depending on the type of connection.)
-
From the drop-down list, select the test to perform on the attribute.
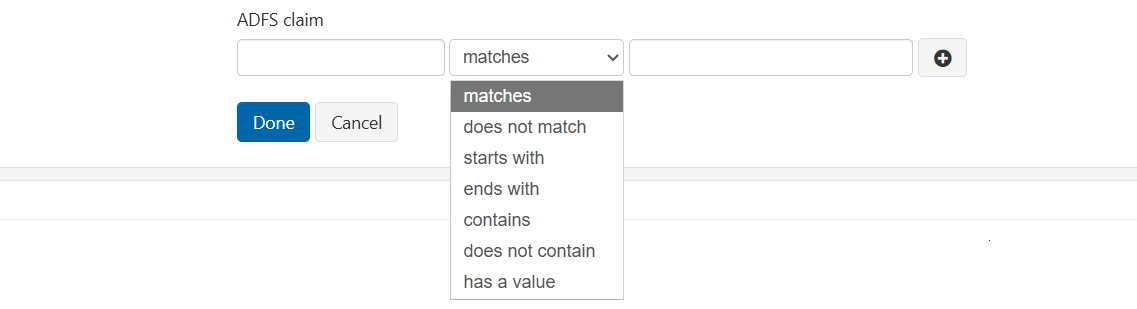
The options are:-
matches
-
does not match
-
starts with
-
ends with
-
contains
-
does not contain
-
has a value
-
-
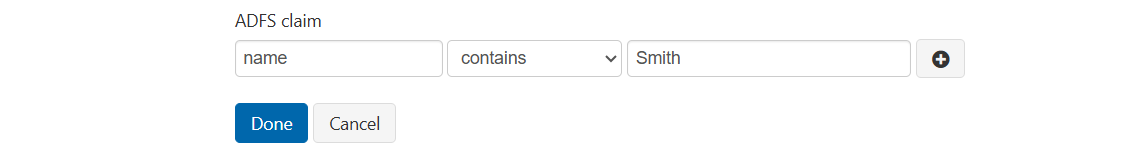
In the last field, enter the required value for the condition. For example, if you wanted to suspend the account of anyone named ‘Smith’, you would enter ‘Smith’ in this field; the complete rule would be something like ‘name | contains | Smith’.
-
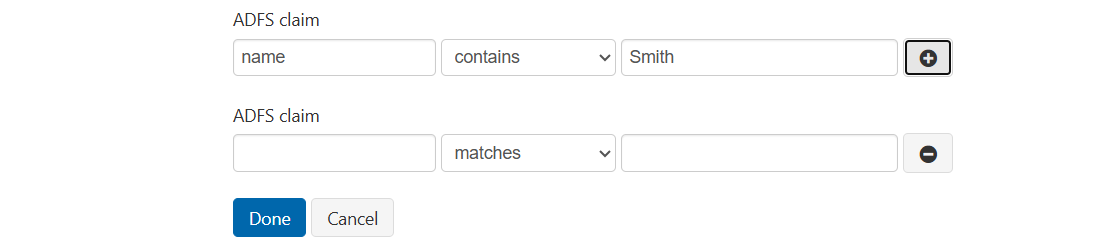
This creates a simple rule with a single condition. To add more conditions for a more complex rule, press the plus button to generate another set of input fields. Repeat as necessary. (If you add fields and then decide not to use them, press the minus button to remove them before you submit.)
-
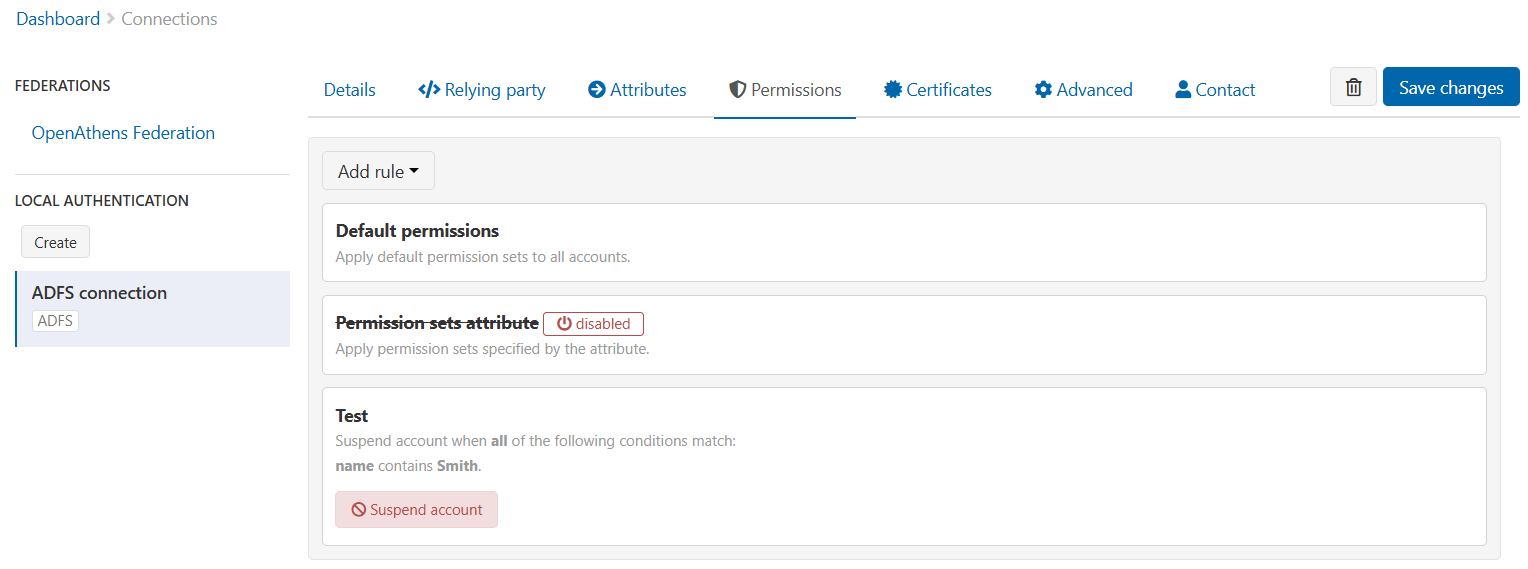
When you’ve finished, press Done. Your new rule appears in the list of rules. Check that the rule is correctly configured.
-
Repeat to add any other rules that are required.
-
Press Save changes to put your changes live.
Edit a suspend rule
-
Go to Management > Connections.
-
Under Local authentication in the left sidebar, select the required local connection.
-
Go to the Permissions tab.
-
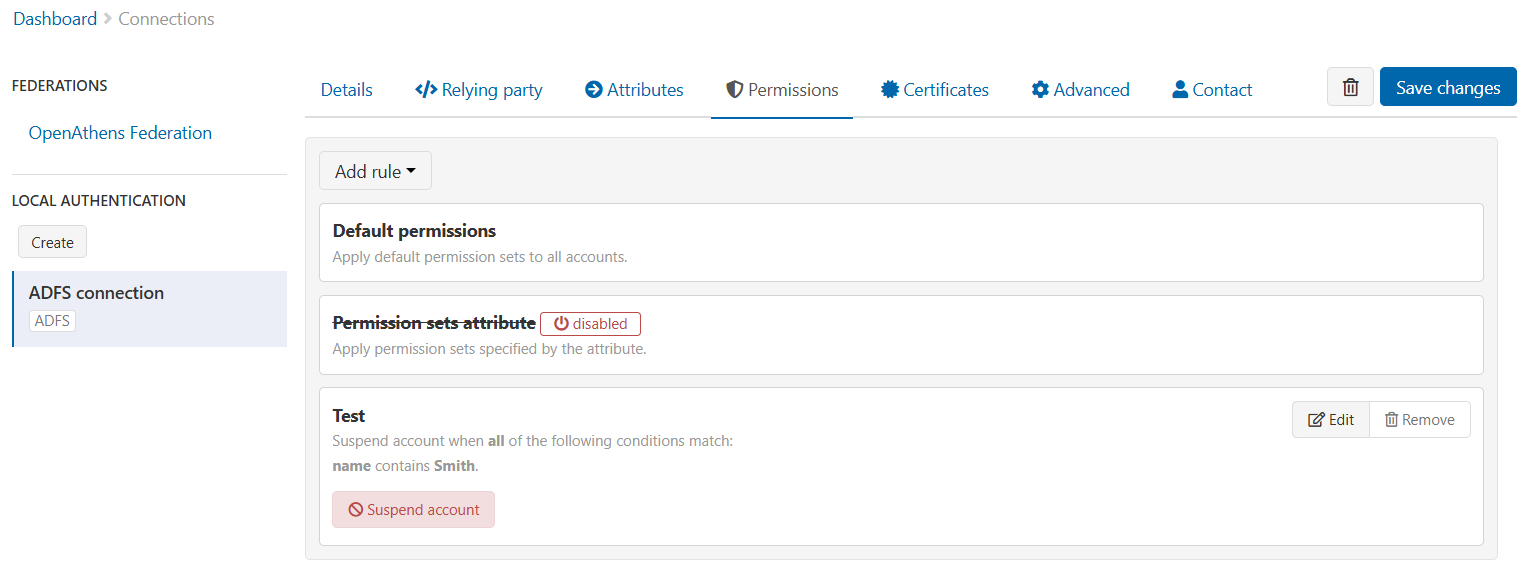
In the list of rules, hover over the rule you want to edit. Edit and Remove buttons appear.
-
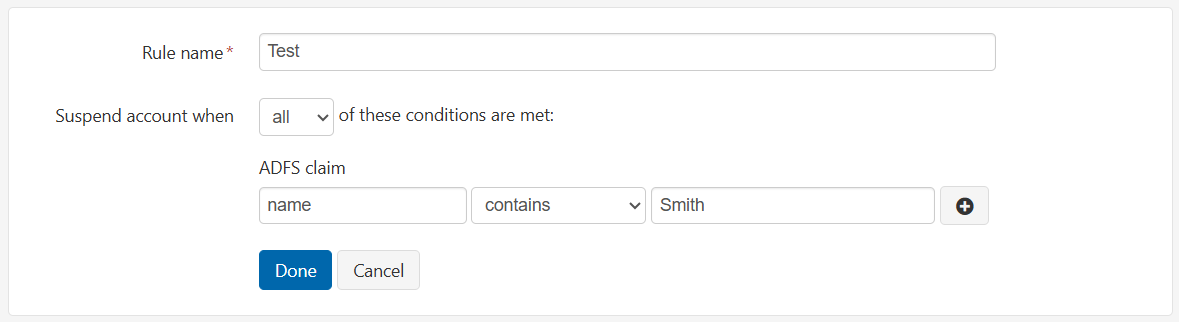
Press Edit. The details of the rule appear on screen.
-
Edit the name or conditions of the rule as required.
-
Press Done. The amended rule is shown in the list.
-
Repeat for any other rules you want to edit.
-
Press Save changes to put your changes live.
Delete a suspend rule
-
Go to Management > Connections.
-
Under Local authentication in the left sidebar, select the required local connection.
-
Go to the Permissions tab.
-
In the list of rules, hover over the rule you want to edit. Edit and Remove buttons appear.
-
Press Remove. You are asked to confirm this action before the rule is deleted.
-
Press Delete to confirm.
-
Press Save changes to put your changes live.
Multi-valued attributes and negative conditions
If your local source has a multi-valued attribute, such as the memberOf attribute from Microsoft Entra ID (aka Azure or Active Directory), be aware of how suspend rules treat this attribute. A multi-valued attribute contains multiple discrete value elements. Suspend rules check each of these values separately, so if even one of them matches the specified condition, then the rule will pass. This can happen even when you might not obviously expect it.
Let’s look back at one of our earlier examples. Assuming memberOf contains multiple discrete values, then we can write a rule that checks for one or more of those values:
Suspend account when any of these conditions are met:
memberOf contains visitor
memberOf contains walk-in
Regardless of what other data the attribute contains, or what order the values are listed, as long as memberOf includes either ‘visitor’ or ‘walk-in’ then the rule will pass.
So far, that is probably what you would expect. However, the rule is doing something subtly different from what its wording might suggest. The rule doesn’t look at memberOf as a whole, to determine if ‘visitor’ or ‘walk-in’ appear somewhere in the list of values. Instead, it tests each value individually, checking if ‘visitor’ contains the required value, if ‘walk-in’ contains the required value, and so on. Each does contain a required value, so the rule passes.
In an example like the former, which tests a positive condition, the outcome is the same as checking the values of the attribute as a whole. Things become more complicated, though, if you want to create a negative condition such as does not contain. This condition will be true if any of the individual values meet it, even if other values indicate a contrary outcome.
For example, say we want to suspend users whose memberOf attribute does not include the value ‘student’. We create the following rule:
Suspend account when all of these conditions are met:
memberOf does not contain student
Let’s assume that there are two users, A and B. A has a memberOf attribute with the values ‘student, alumnus’. B has the memberOf attribute ‘visitor'.
Which users are suspended by the rule? We might expect that B is suspended while A gets to keep her account. Actually, both are suspended. Why? The rule checks against each of the discrete values in memberOf individually. User A meets the specified condition since, although she has the value ‘student’, she also has ‘alumnus’, which matches the criterion of does not contain student. Because a match for any value triggers the rule, A is culled along with B.
As you see, this behaviour can be counter-intuitive, although it does have potential uses. Take care when creating negative conditions with multi-valued attributes and check that your rule will not produce undesirable results.
Multi-valued attributes are different from multi-line attributes, in which a single value element is split into several parts.