The function or feature discussed below is experimental, and may be changed or withdrawn.
The authentication point has a debug mode that allows you to perform a couple of useful functions.
For all:
-
See exactly which attributes are being passed to a service provider, so that you can confirm how your release policy is working and test changes
For local authentication users:
-
View the attributes being passed to OpenAthens by SAML connections such as ADFS
-
View and interact with local authentication connections that are not yet marked as live, e.g. when adding a new one or migrating from an old one
Enable debug mode
You activate or deactivate debug mode by using a bookmarklet called OpenAthens SSO Debug.
Get the bookmarklet
If you don’t already have the bookmarklet, add it to your browser first.
-
Go to our Enable SSO debug page (https://login.openathens.net/resources/static/ssodebug.html).
-
Drag the highlighted link OpenAthens SSO Debug to your bookmarks bar.
Turn on debug mode
Before using debug mode, you must turn it on in your browser. Once turned on, debug mode will remain active either until you turn it off or until you close the browser (depending on your browser settings).
-
Go to any page on the domain login.openathens.net. The password reset page is a convenient choice.
-
Click the OpenAthens SSO Debug bookmarklet in your bookmarks list. A message confirms that debug mode is now turned on.
-
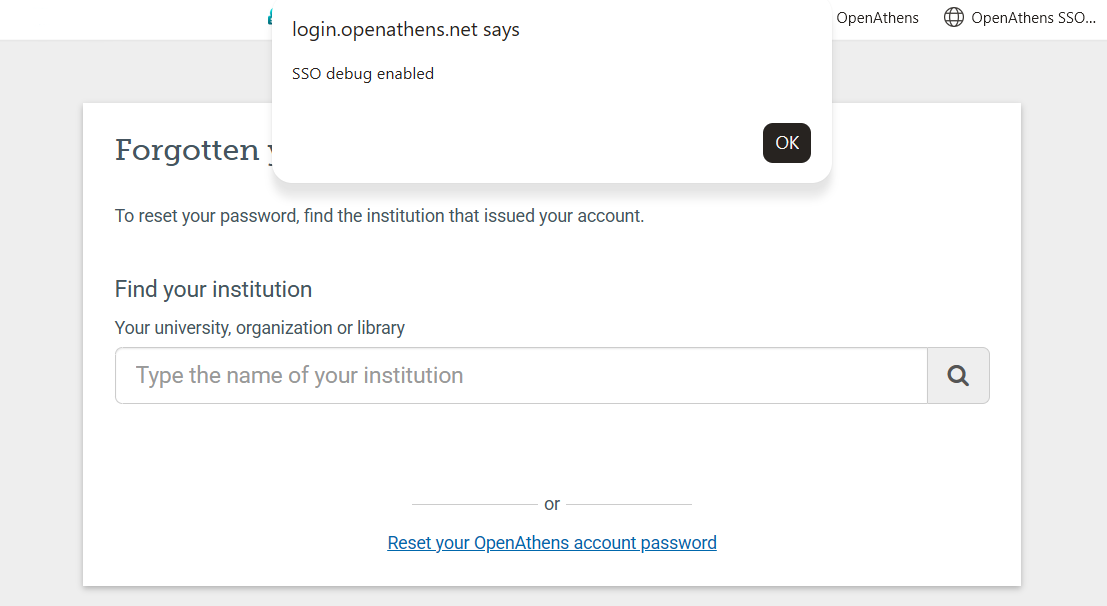
Press OK to dismiss the message.
To turn off debug mode, repeat this process. Clicking the OpenAthens SSO Debug bookmarklet while debug mode is turned on will disable debug mode.
View debugging output
With debug mode turned on in your browser, access the resource you want to check. The debug tool interrupts the transfer to show you details of the attributes being released. You can then choose whether or not to continue to the resource.
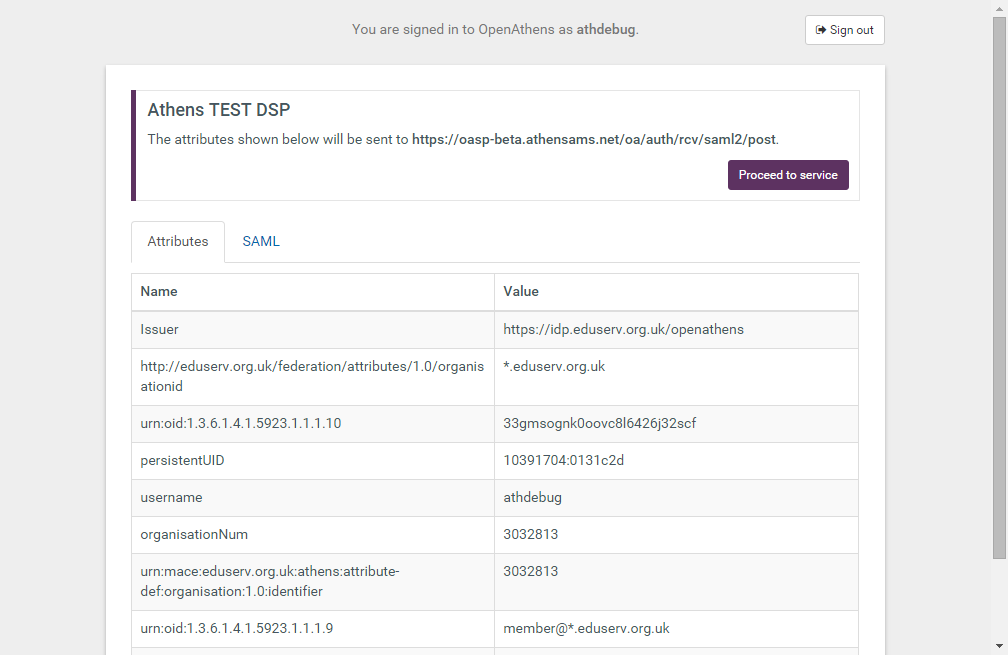
The Attributes tab shows attributes as a table. To view the data as SAML, go to the SAML tab.
Local connections view
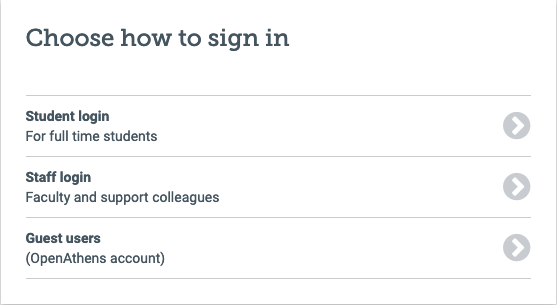
If you have multiple local connections and none of them is set as the default, the authentication point will display available connectors in an overlay (including any not marked as live or visible). If you select a SAML based connector, debug mode will show you which attributes the connector is sending to OpenAthens.
To see the available connections, you first need to search for your organisation at the authentication point, use a WAYFless URL or access a resource.
Anything to watch out for?
With local connectors, debug mode can show only incoming attributes from SAML based sources, not things like the API or LDAP.
If you have only one local connection and it is LDAP or SirsiDynix, you will not see the overlay because these connection types can accept OpenAthens accounts. You will only be able to tell the difference if you modify the username and password labels on the login page tab of the connection.
If you do this while accessing a resource, you will interrupt a time-stamped SAML response. If you do not proceed to the resource within a minute, access is likely to fail.
If the request and response use SAML 2, the key attributes are passed using the format urn:oid format. In this format, each attribute is distinguished by the last number in its name, for example:
|
Name |
Passes |
May have been previously known as |
|---|---|---|
|
urn:oid:1.3.6.1.4.1.5923.1.1.1.1 |
Role (e.g. member, staff, student) |
eduPersonScopedAffiliation / Scoped Affiliation / Affiliation |
|
urn:oid:1.3.6.1.4.1.5923.1.1.1.7 |
Entitlement values |
eduPersonEntitlement / Entitlement |
|
urn:oid:1.3.6.1.4.1.5923.1.1.1.10 |
The targeted ID value |
eduPersonTargetedID / Targeted ID |
The older urn:mace format should be seen only if a service provider makes a SAML 1 request.
If debug mode is active when you sign in to the Compass admin area, it will also output details of that login. However, you are unlikely to need this information.